Random Notes on Bug Bounty Tools That Actually Work
A few tools I reach for every day in my bug bounty workflow: httpx, notify, anew, Param Miner, hakrawler, jq/cut/awk, Logger++ and GitHub recon, with the exact flags I use.
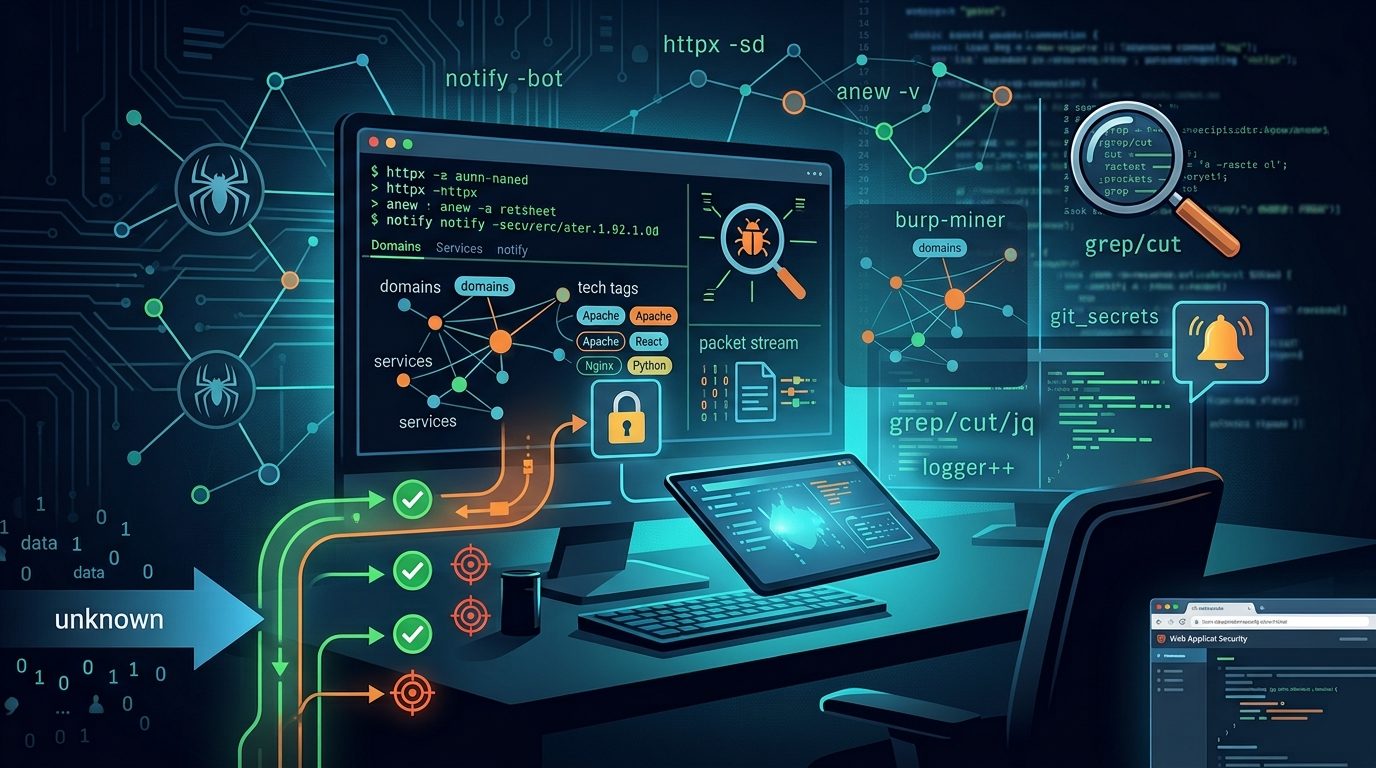
A few tools I reach for every day in my bug bounty workflow: httpx, notify, anew, Param Miner, hakrawler, jq/cut/awk, Logger++ and GitHub recon, with the exact flags I use.
Two simple but high-impact findings, and the lessons that led me to them.
Crawling a target I thought I knew — with Katana, hakrawler, waybackurls, and unfurl — surfaced a hidden /HelpApi/ endpoint and an IDOR leaking users' PII.
A reality check on bug bounty and the myth of easy money.
A field guide to web cache attacks — from CP-DoS tricks (oversize headers, meta characters, method override, unkeyed ports, redirect DoS) to poisoning with XSS payloads and web cache deception via path confusion.
A Broken Access Control bug on a chess platform, via request interception and cookie swapping.
Why JavaScript files are a goldmine for bug hunters — the tools (JSleak, JSecret, jsluice), the workflow, and the resources I use to dig secrets, endpoints, and client-side bugs out of JS.
A forgotten subdomain, a Shodan dork, and a single PUT request — how one overlooked endpoint led to an information disclosure and then an IDOR into users' video session data.